SageShield Space
A configuration and management software based on underlying security chip technology, visualizing chip command dispatch and execution tracking.
Hard Encrypt · Hard Hide · Hard Destroy — Chip-level intrinsic security
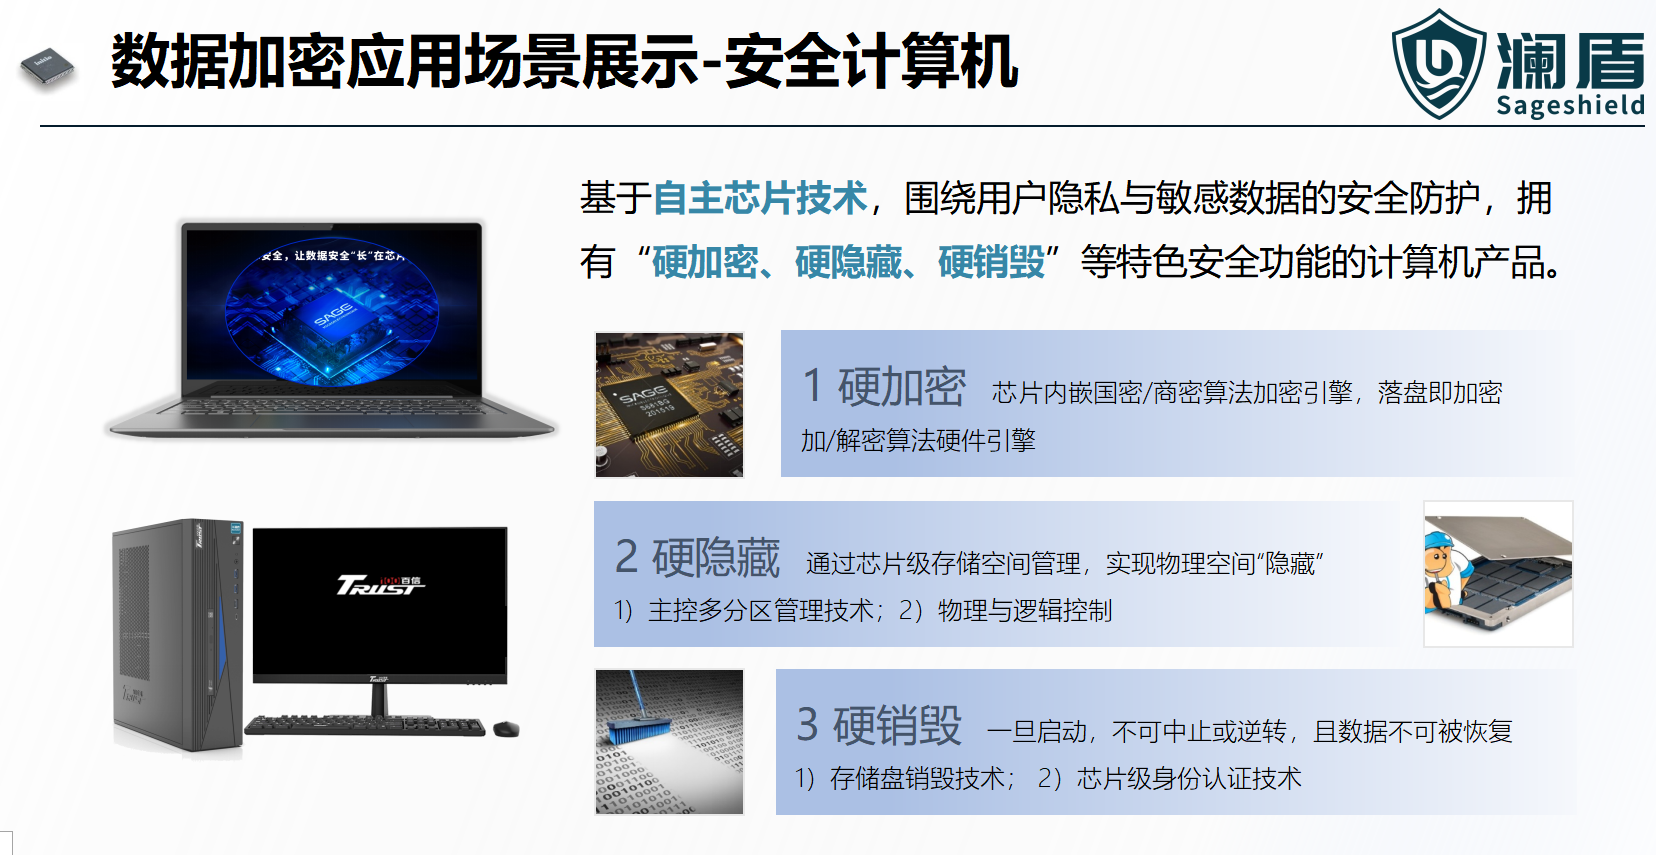
A secure computer based on self-owned chip technology, sinking security to the hardware level, building "hard encrypt, hard hide, hard destroy" intrinsic security, providing disk encryption, SM algorithms, secure partition, host binding, data destruction, management platform and log audit without relying on the OS.
A configuration and management software based on underlying security chip technology, visualizing chip command dispatch and execution tracking.
The security chip embeds a crypto engine with SM algorithms. Data is SM4-encrypted before being written to disk, stored as ciphertext — true disk encryption.
A "hard hidden" storage space based on self-owned chip technology, independent of the OS: invisible in BIOS/disk tools, unrecognizable by file managers, cannot be formatted or deleted.
The security chip binds HDD and host 1:1. When the bound HDD is moved to another device, it is invisible and unreadable before correct authentication.
Supports software erase and physical medium destruction, real-time or scheduled. The process is irreversible — once triggered, it cannot be stopped and data cannot be recovered.
Unified management of SageShield® secure computers: register/logout, hardware/system info, key management, partition enable/disable, online status, operation snapshots, security policies.
Read-only recording of all operations: key input, data read/write, settings, etc. — who did what and when, stored in the secure partition for audit.
Tested and adapted with domestic CPUs (Phytium, Hygon, Zhaoxin, Kirin), OS (UOS, Kylin), databases (Kingbase, Dameng), middleware (Tongtech, Kingdee, BES) and office suites (WPS, Yongzhong, Foxit, Shuke).
Get datasheets, sample requests and technical support, please contact us